


Executive summary
On 13 October 2026, the European Data Protection Board issued preliminary guidance explaining how the GDPR applies to smart glasses. Although not binding legislation, the statement clarifies regulatory expectations concerning recording and connected AI services.
Users, manufacturers and service providers may each bear responsibility for processing personal data for smart glasses. Where the GDPR applies, processing requires a lawful basis before collection. Consent cannot be inferred from silence, while legitimate interests require necessity and careful balancing against individuals’ rights.
Organisations should combine clear recording signals with accessible privacy information, limit collection and retention, and provide effective ways to exercise data protection rights. Particular care is needed around children, sensitive locations and biometric identification.
The development of smart glasses regulations and its legal significance
On 13 October 2026, the European Data Protection Board (EDPB) adopted Statement 1/2026 on smart glasses. The statement addresses eyewear equipped with cameras, microphones and connected services, including artificial intelligence. Such devices can assist communication, translation and navigation, but can also collect information about people who do not realise they are being recorded.
The statement explains how existing data protection obligations apply to these activities and identifies practical safeguards for manufacturers, service providers and users.1
The statement is a preliminary, non-binding regulatory guidance. It neither creates a new offence nor imposes a general prohibition on smart glasses. Its importance is nevertheless substantial because it sets out the collective position of European data protection regulators and gives organisations a clear indication of compliance concerns.
This legal report also considers the EU General Data Protection Regulation (GDPR) in the context on smart glasses.2 Please note that national privacy, employment and criminal laws may impose additional restrictions, including where the GDPR does not apply.
Why smart glasses require particular attention
The principal concern is the gap between the wearer’s ability to collect information and a bystander’s ability to recognise or challenge that collection. Ordinary-looking eyewear can record faces, conversations and surroundings with little visible interruption. AI services may analyse the same information remotely. Hospitals, schools and workplaces present particular risks because recordings can expose confidential information, capture children or discourage people from speaking freely.3
The accompanying study by sociologist Yann Bruna gives this situation some useful context. Based on interviews with 22 people, including seven users and fifteen non-users, it describes recordings made to preserve evidence, anticipate disputes and monitor others.4
These qualitative findings illuminate possible harms; they do not establish how common those practices are across Europe. The study was commissioned through the EDPB’s Support Pool of Experts, but its conclusions are the author’s and are not the Board’s official position.
Information acceptable within one setting may become intrusive when collected or distributed in another.5 Applied here, being visible in a street does not mean expecting a conversation to reach an AI provider or an unrestricted online audience. This distinction supports scrutiny of reasonable expectations and subsequent uses.
Who bears responsibility?
Responsibility depends on who determines why and how personal data are processed. A wearer of the glasses, an employer or a connected service provider may be a controller, meaning the person or organisation responsible for those decisions. In fact, more than one user may share that role.
Manufacturing the hardware does not automatically make a company responsible for every recording; equally, describing processing as user-controlled cannot remove responsibility for operations the company itself determines.6
Such an assessment should follow the data through each stage including capture, transmission, analysis, storage and publication. Parties may have different roles at different stages. For example, a service that analyses an image for its own defined purpose cannot simply rely on the wearer’s private use to avoid scrutiny. Contracts can allocate practical tasks, but cannot displace responsibilities established by the actual processing arrangements.
Individuals benefit from the GDPR’s household exemption only when processing is purely personal or domestic. The statement gives private sharing with family or friends and personal translation in a private setting as examples.

Nonetheless, uploading footage to a public social media account, or using glasses for professional activities, generally falls outside that exemption. The assessment remains sensitive to the circumstances.7
The exemption must be interpreted narrowly.
In the Ryneš case, the Court of Justice of the EU held that domestic security surveillance extending into public space was outside the household exception under the GDPR’s predecessor.8
That judgment does not make every holiday photograph subject to the GDPR, but it undermines any assumption that personal ownership alone exempts outward-facing surveillance. Providers processing data for their own purposes remain subject to the GDPR even when the wearer’s activity is exempt.
A lawful basis is required before data collection
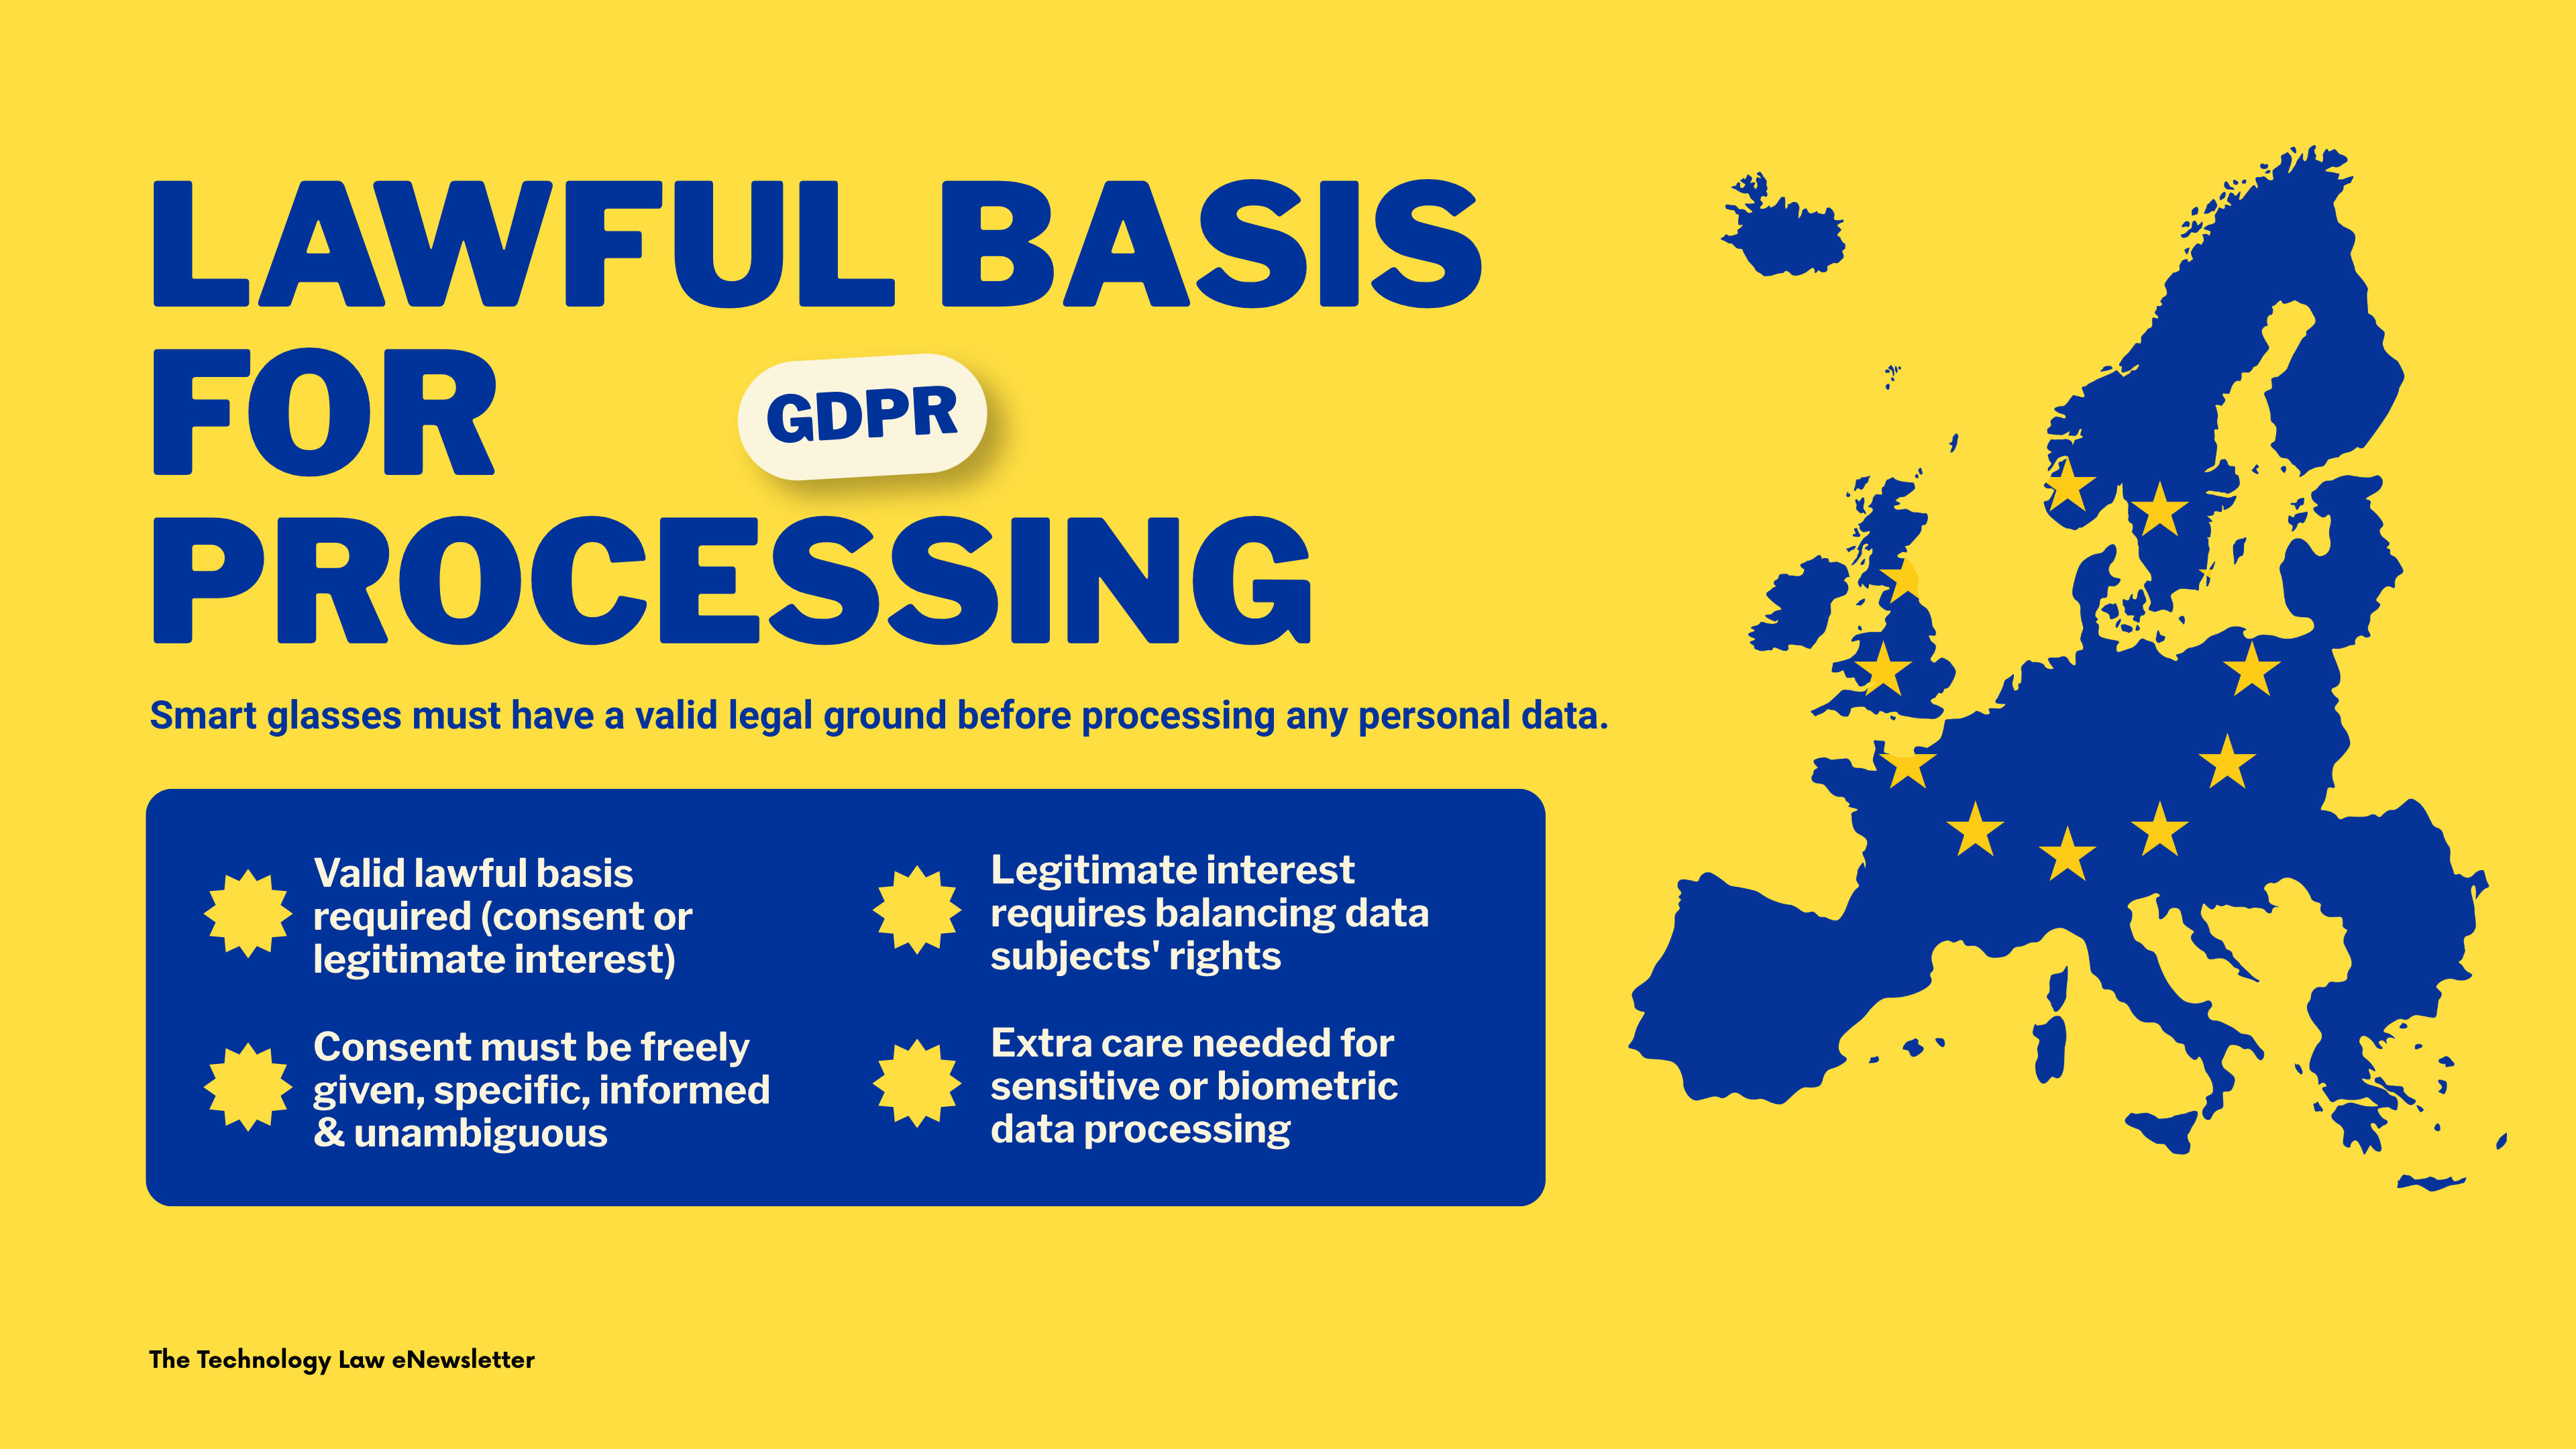
Where the GDPR applies, each processing operation requires a lawful basis. Consent may support a recording in an appropriate setting, but it must be freely given, specific, informed and unambiguous. Remaining nearby, noticing a light or failing to object does not establish consent.
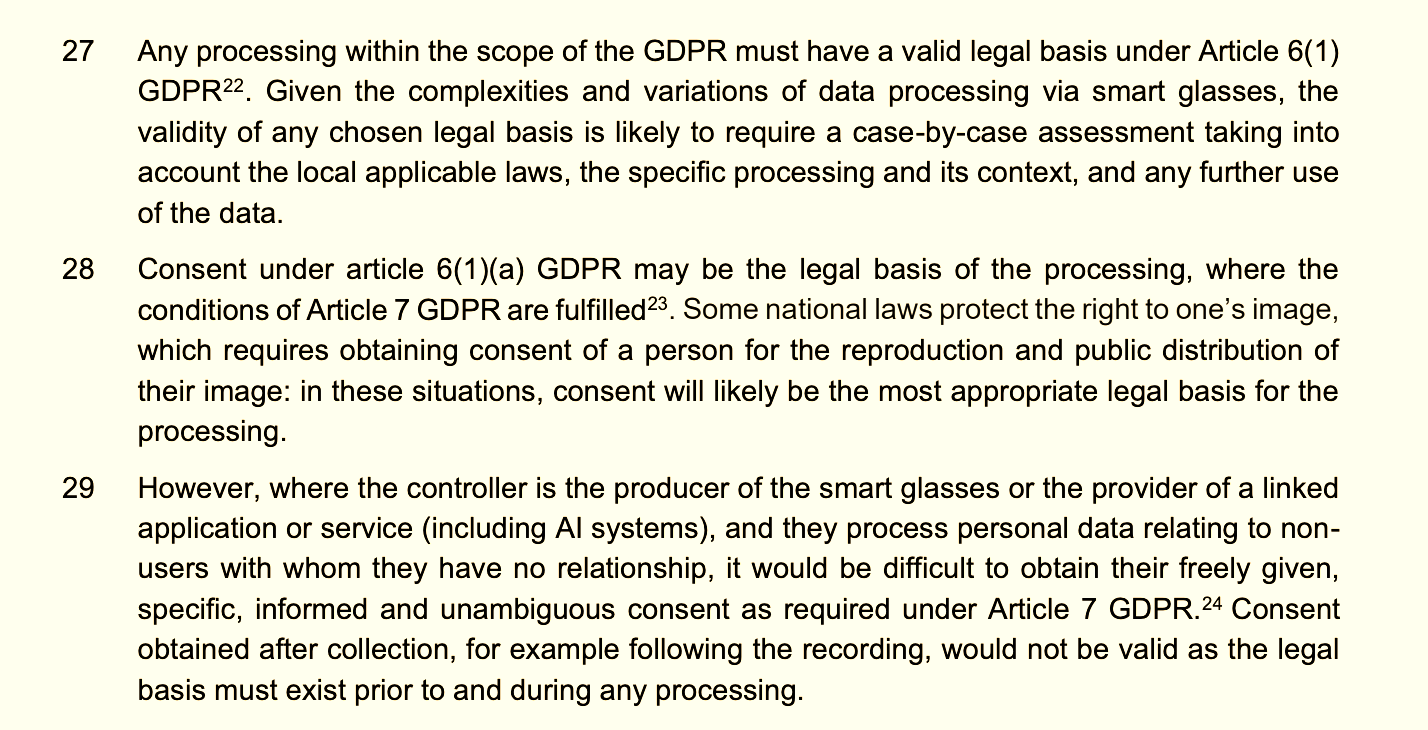
The EDPB expressly rejects obtaining consent after recording as a way to legitimise the original collection. Permission from the purchaser also cannot substitute for consent from identifiable bystanders.9
Legitimate interests may provide another basis for the use of smart glasses, but only after identifying a legitimate purpose, demonstrating necessity and balancing that interest against the affected person’s rights.
A specific need to document an incident may justify more than a general wish to record everyone for personal security. The statement warns that hypothetical safety concerns alone cannot justify continuous or indiscriminate recording. Less intrusive alternatives, the location and the involvement of children will influence the assessment.10
Further commercial use presents a separate problem. A provider cannot assume that information captured for translation or assistance is freely available for advertising or AI training. Purpose limitation and the rules governing further processing must be considered.
The EDPB identifies particular difficulty in relying on legitimate interests for unexpected secondary uses involving bystanders. Providing more information does not, by itself, make such processing reasonably expected or lawful.11

Transparency must work for people nearby
From our preliminary assessments, it seems the EDPB statement’s most concrete contribution concerns notice at the moment of collection. A privacy policy shown only to the purchaser cannot adequately inform people passing the device.

The EDPB recommends combining conspicuous visual indicators, audible signals, recognisable design and, where appropriate, proximity notifications. Indicators should work in different lighting conditions, remain active long enough to be understood and resist interference. It recommends preventing recording when the indicator is covered.12
These mechanisms makes it clear that processing occurs; they do not necessarily explain who controls the data, why it is collected, how long it is retained or how rights can be exercised.
Controllers are advised to also provide the applicable GDPR information. Existing EDPB guidance on video devices supports layered notices, with essential information immediately available and fuller details accessible separately. Designing a workable equivalent for mobile eyewear remains a significant practical challenge.13
Proximity applications cannot be the only solution. They exclude people without compatible devices and must avoid creating a new means of tracking wearers.
Accessibility also matters too since too much light may impact someone with impaired vision. Standardised processes could improve recognition, but industry standards would support compliance rather than replace the underlying legal duties.14
Transparency must also connect the recording to an effective route for exercising rights. A bystander who knows only that a camera is active may still be unable to identify the controller or locate a recording.
Our recommendation is that organisations should test whether their arrangements work for someone who has no registered account with the service. Requiring that person to become a customer would leave the underlying problem unresolved.
Safety measures and organisational consequences
This legal report suggests a practical solution which should begin with limiting data collection using smart glasses.
The EDPB recommends processing on the device where possible, obscuring bystanders and restricting retention. For smart glasses intended to provide immediate assistance, long-term data storage should ordinarily be disabled by default unless necessary for the function or deliberately activated with safety requirements.
Our suggestion is that it may be necessary to consider the blurring of identifiable details before sharing a recording so as to reduce privacy risks. However, the original recording must still have been collected lawfully.15
Additional rules apply to sensitive processing. A photograph is not automatically biometric data within GDPR article 9, but technical processing for unique identification can trigger its restrictions.
Processing health information or other protected categories also requires an applicable article 9 condition alongside an article 6 basis.
Controllers must assess whether a data protection impact assessment is required before deployment; article 35 expressly includes systematic monitoring of publicly accessible areas on a large scale.16
A data protection impact assessment should examine necessity, proportionality and realistic safety measures, including the consequences for people who cannot avoid the smart glasses.
The requirement depends on the proposed processing and its risks, rather than the product’s name alone. Where high residual risks require prior consultation, the controller must engage the competent supervisory authority before processing begins.17
We also recommend that employers and institutions should establish clear rules on permitted functions, sensitive locations, access to recordings and deletion. They should examine connected providers, security arrangements and international transfers, rather than assessing the glasses in isolation.
Procedures must enable people to request access, seek erasure where applicable and object to processing based on legitimate interests. An objection is not always an absolute veto, but it requires a substantive response.18
Other legal frameworks require separate attention. The statement notes that the ePrivacy rules may apply to certain operations involving terminal equipment. Domestic rules on image rights, confidential conversations and workplace monitoring may also affect a deployment.
Conversely, recording for journalism can engage freedom of expression and applicable national exemptions under article 85 GDPR. Neither a claim to be gathering evidence nor a journalistic label provides automatic permission for unrestricted recording or publication.19
From our perspective, the EDPB statement provides a useful foundation, but it leaves some unanswered questions about effective mobile notices and enforceable bystander rights.
It is important to note that EU regulators still retain existing powers to restrict unlawful processing and impose penalties under the GDPR.
Employers and institutions using smart glasses should review how the devices are used and whether that use complies with data protection law. The central requirement is to demonstrate that a useful wearable function can operate with justified collection, understandable notice and safety measures that protect everyone whose information it processes.
This means manufacturers should address privacy during smart glasses product design and provide safeguards that function effectively throughout the device’s ordinary operating life.19
EDPB, EDPB statement on the data protection challenges of smart glasses (13 October 2026); Statement 1/2026 on Smart glasses (13 October 2026), paras 1-5.
EDPB, Statement 1/2026, paras 1, 15, 34-36. On the Board's guidance function, Regulation (EU) 2016/679 (GDPR), art 70(1)(e).
EDPB, Statement 1/2026, paras 6-10 and 21-23.
Yann Bruna, The connected gaze. Video recording, surveillance and administering evidence in the age of smart glasses (SPE report, published 1 October 2026), pp 2, 5-10, 14-15 and 24-33.
Helen Nissenbaum, 'Privacy as Contextual Integrity' (2004) 79 Washington Law Review 119, especially the discussion of contextual norms of information gathering and distribution.
GDPR, arts 4(7) and 26; EDPB, Statement 1/2026, paras 11 and 16-18.
GDPR, art 2(2)(c); EDPB, Statement 1/2026, paras 12-14.
Case C-212/13 Ryneš v Úřad pro ochranu osobních údajů, EU:C:2014:2428, paras 29-33; GDPR, recital 18; EDPB, Statement 1/2026, paras 14 and 16-18.
GDPR, arts 4(11), 6(1)(a) and 7; EDPB, Statement 1/2026, paras 27-29.
EDPB, Statement 1/2026, para 30, and para 33; GDPR, art 6(1)(f).
GDPR, arts 5(1)(b) and 6(4); EDPB, Statement 1/2026, paras 19 and 30.
EDPB, Statement 1/2026, paras 20-26.
EDPB, Guidelines 3/2019 on processing of personal data through video devices, version 2.0 (adopted 29 January 2020; correction 26 February 2020), paras 110-117; Statement 1/2026, paras 23-24.
EDPB, Statement 1/2026, paras 20-26 and footnotes 17 and 19.
EDPB, Statement 1/2026, paras 32-33; GDPR, arts 5(1)(c), 5(1)(e) and 25.
GDPR, arts 4(14), 9 and 35(1), (3)(c); EDPB, Guidelines 3/2019, paras 72-76.
GDPR, arts 35(1), 35(7) and 36(1).
EDPB, Statement 1/2026, paras 10 and 31-34; GDPR, arts 15, 17, 21, 28, 32 and 44-49; EDPB, Guidelines 3/2019, paras 105-106.
EDPB, Statement 1/2026, paras 28, 32 and 34; GDPR, art 85. National exemptions and other domestic restrictions require assessment in the relevant jurisdiction.